Financial Services SaaS Security
Financial institutions face some of the most stringent security and compliance requirements in any industry. With customer financial data, regulatory oversight, and the constant threat of cyber attacks, your SaaS security must exceed industry standards. SaaS Security Score provides financial services-specific assessments that align with SOX, GLBA, PCI-DSS, and other critical financial regulations.
Financial Industry Challenges
- Customer financial data protection across multiple platforms
- SOX, GLBA, and PCI-DSS compliance requirements
- Real-time transaction security and fraud prevention
- Third-party vendor risk management
- Regulatory reporting and audit requirements
- Incident response and breach notification
- Customer privacy and data residency requirements
- Integration with legacy financial systems
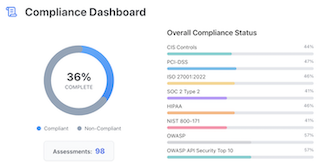
Financial Compliance Framework Support
SOX (Sarbanes-Oxley)
Internal controls over financial reporting and IT security controls assessment.
GLBA (Gramm-Leach-Bliley Act)
Customer financial information privacy and security requirements.
PCI-DSS
Payment card industry data security standards for financial transactions.
FFIEC Guidelines
Federal Financial Institutions Examination Council cybersecurity standards.
NYDFS Cybersecurity
New York Department of Financial Services cybersecurity requirements.
ISO 27001
Information security management system standards for financial organizations.
NIST Cybersecurity Framework
Risk-based approach to managing cybersecurity risk in financial environments.
Basel III
International banking regulations including operational risk management.
Financial Services-Specific Features
- Customer financial data protection analysis
- Transaction security and fraud prevention assessment
- Third-party financial vendor risk evaluation
- Regulatory reporting and compliance monitoring
- Incident response and breach notification planning
- Customer privacy and data residency compliance
- Integration security with legacy financial systems
- Executive and board-level security reporting
Why Financial Institutions Choose SaaS Security Score
Regulatory Expertise
Built specifically for financial compliance with pre-configured regulatory controls.
Rapid Assessment
Get comprehensive security insights in under 10 minutes, not weeks or months.
Continuous Monitoring
Ongoing security scoring and alerting for proactive risk management.
Executive Reporting
Clear, actionable reports for financial leadership and compliance officers.